Early access, FedRAMP Rev 5 baseline
FedRAMP authorization, managed as one lifecycle
SecurITPosture takes a cloud system from onboarding and boundary definition through evidence, scanning, the System Security Plan, assessment, and the POA&M in a single governed record. AI drafts. People approve.
No cloud credentials are stored. AWS is reached through an IAM role assumed with STS, scoped to read, and only encrypted connection metadata is kept.
Built to the rules
FedRAMP Rev5 and the 2026 rules in one product
- FedRAMP 2026 rules in the product, version 2026.07.14.01
- 246
- Key Security Indicators tracked
- 46
- 2026 package documents generated as validated JSON
- 5
- Rev5 FedRAMP templates filled in place
- 7
One record
From the questionnaire to continuous monitoring
Data entered once propagates to every downstream document. The questionnaire feeds the SSP, the SSP feeds the SAP and SAR, and findings feed the POA&M.
- 1QuestionnaireThe single source of the organization and system facts
- 2System Security PlanDrafted from evidence, reviewed by people
- 3AssessmentSAP, test cases, SAR, and the Risk Exposure Table
- 4PackageRev5 templates or the 2026 machine readable files
- 5MonitoringScans, indicators, and the quarterly report
Platform
One record, from questionnaire to authorization package
Evidence to control correlation
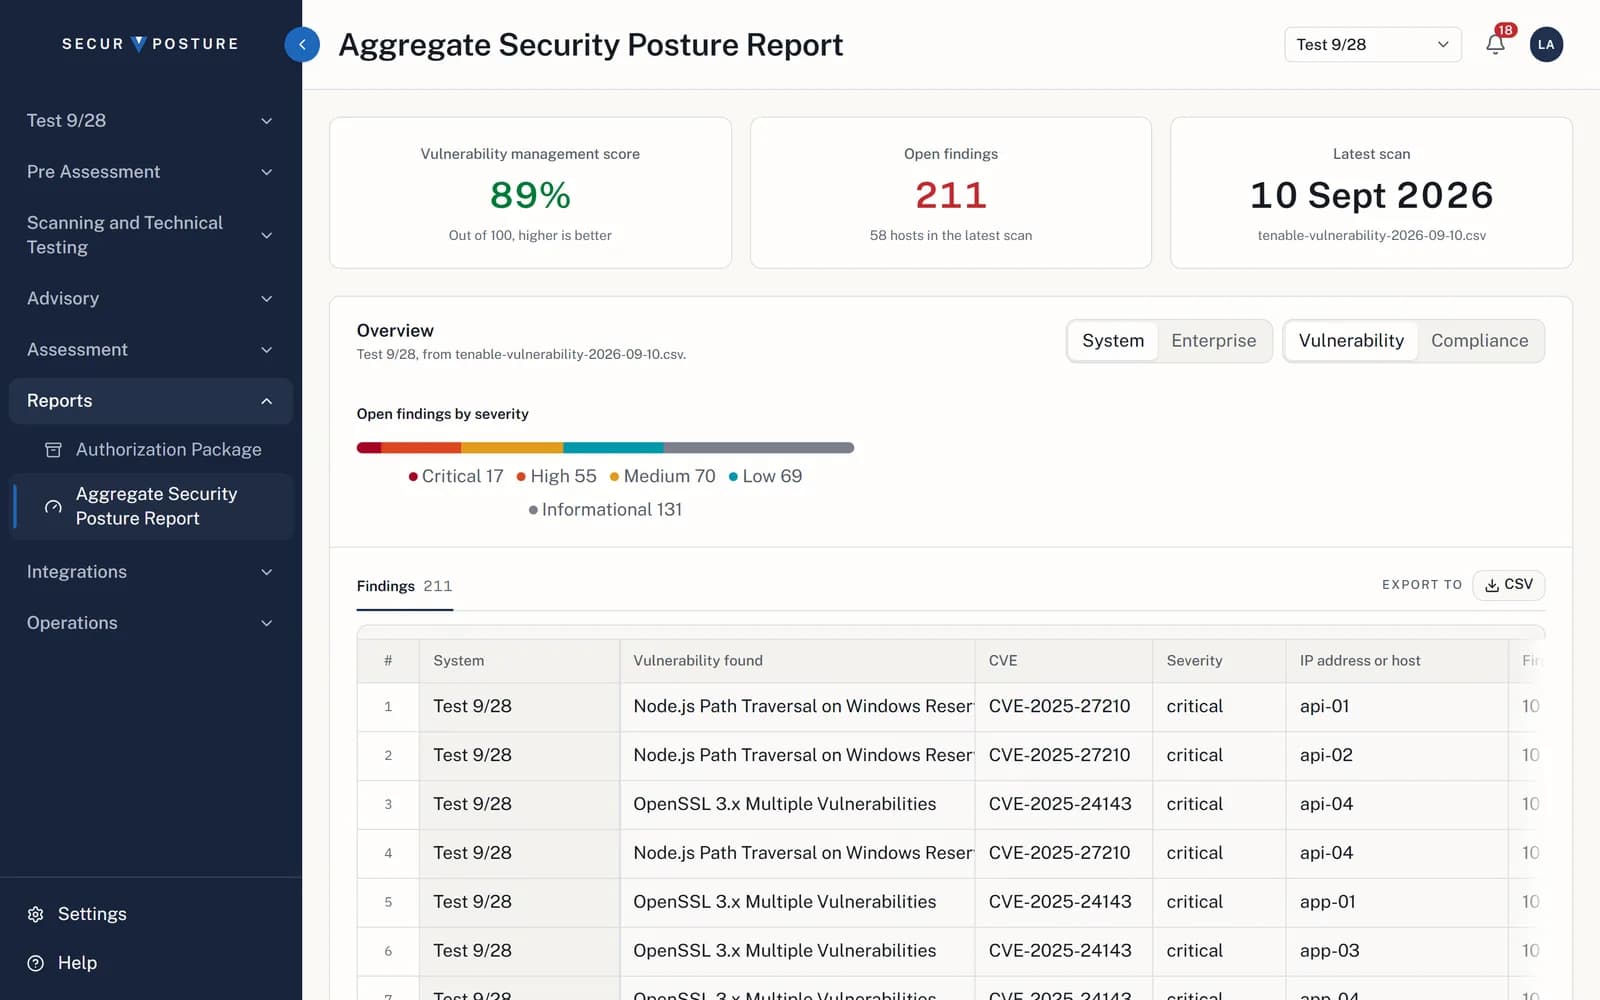
Uploaded evidence and discovered resources are mapped to the controls they satisfy, with a confidence score a reviewer can see.
Scan ingestion and drift
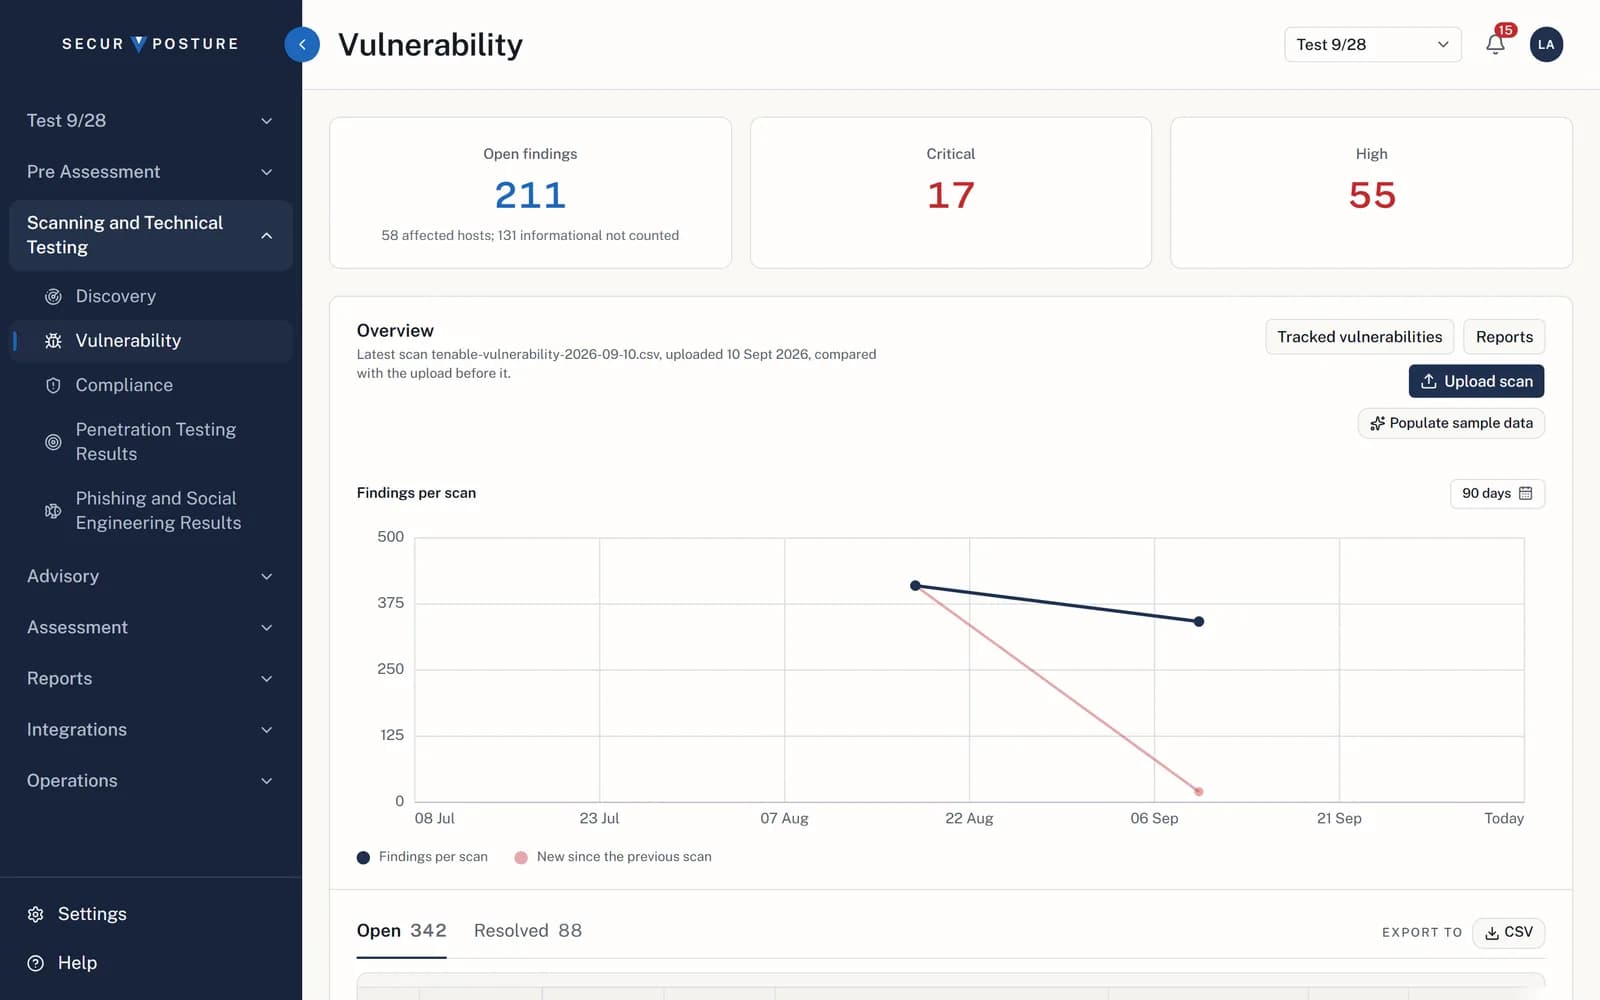
Each Tenable export is compared with the inventory and the previous run.
SSP and control statements
Implementation statements and narrative are drafted from correlated evidence and regenerate when inputs change.
Lifecycle
The lifecycle, and what each level hands to the next
Each level consumes the validated output of the one before it, so the package is traceable from the first record to the last signature.
Foundation
The customer profile, a dedicated tenant, organization and cloud account registration, and the policies that govern the rest.
Integration
AWS is connected by an IAM role assumed with STS. The boundary is defined, the package container created, inherited controls identified.
Evidence
One repository for plans, diagrams, and procedures, each linked to the systems and components it supports. Gaps are flagged before an assessor finds them.
AI and analysis
Tenable exports are compared with the previous run. Evidence is correlated to controls. Implementation statements are drafted and tagged AI Generated.
Assessment
Assessors work the SAP, test cases, SAR, Risk Exposure Table, and POA&M on the same record the analysts built.
Remediation
Each finding takes a remediation path or a documented exception. States move from Open to Closed and feed the POA&M.
Governance
Drafting is automated. Approval is not
The tool drafts and correlates. Authority stays with the reviewer, the assessor, and the approving official.
AI output stays AI Generated until reviewed
Every drafted statement, narrative, and correlation carries an AI Generated tag. Only Human Approved content is consumed downstream, and it returns to AI Generated if regenerated.
Roles separate creator from approver
Customer users, compliance analysts, assessors, administrators, executives, and approving officials each see what their role permits. Whoever creates a record does not approve it.
Every change is audit logged
Actor, action, target, and UTC time for each mutation, integration event, and approval. Audit history is retained after the record it describes is removed.
Where we are
In development with launch partners
SecurITPosture is in early access. We are building it with a small number of organizations preparing Rev 5 packages, and we would rather tell you where we are than imply otherwise.
Readiness check
Fourteen questions, scored by lifecycle area
A short self check across the boundary, inventory, evidence, scanning, and documentation, one question at a time. The score is computed in your browser. No account, nothing stored.
Demo
Bring your boundary diagram and your last SAR
A 45 minute walkthrough with the team that builds the product, on a system shaped like yours. No slides.